Hackers Breached an Email Filter Many IT Providers Use, and Quarantined Mail Has Been Locked Since Monday
N-able, a major vendor that IT providers use to run their clients' spam filtering, confirmed that attackers got into a server behind its Mail Assure and SpamExperts cloud services. Email still flows, but since November 16 businesses haven't been able to sign in, review logs or release quarantined messages, and N-able says credentials stored on the platform may have been exposed. Here is what that means if your IT provider uses it, and the five things to check this week.
- n-able
- mail-assure
- spamexperts
- email-security
- supply-chain-attack
- msp
- quarantine
- credentials
- cybersecurity
- smb
- managed-it
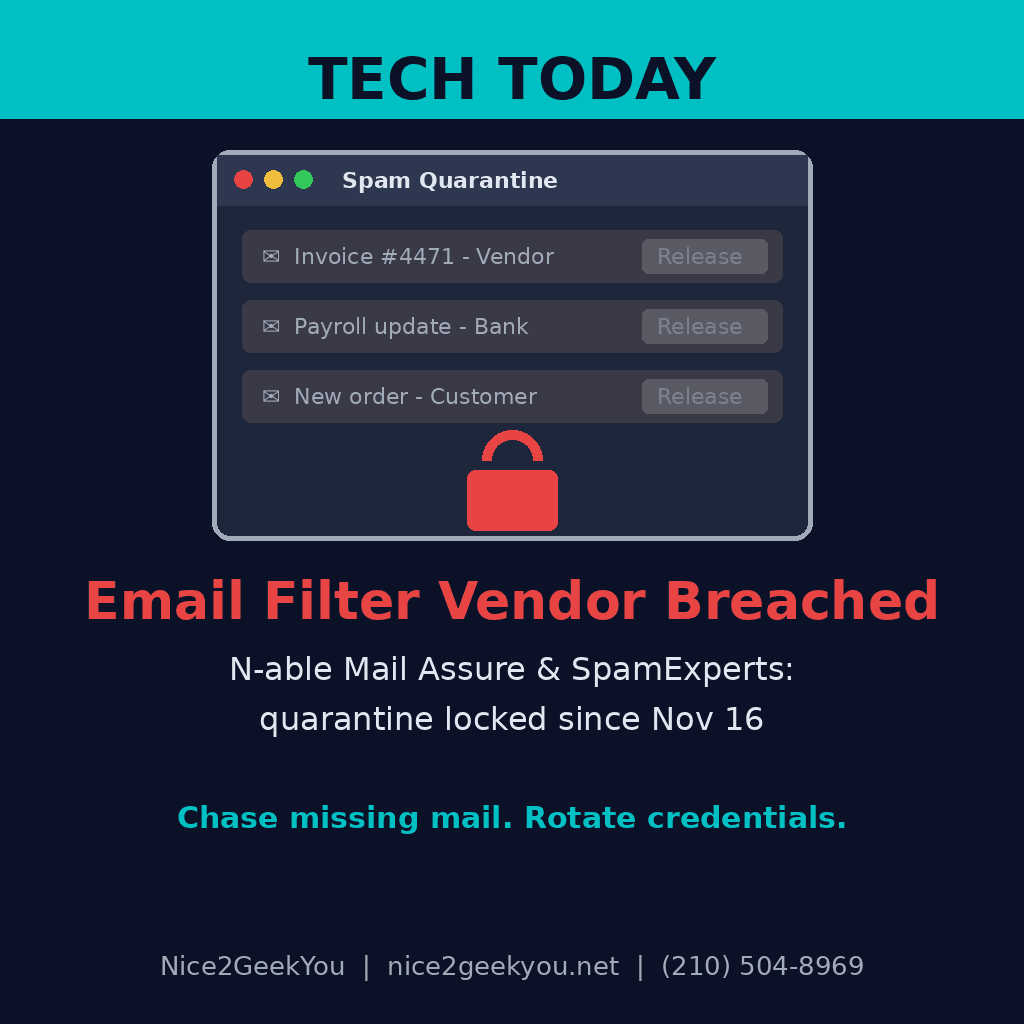
What if the invoice, payroll change or customer order you're waiting on is sitting in a spam quarantine nobody can open? That has been the situation since Monday, November 16, for businesses whose email is filtered by N-able Mail Assure or SpamExperts Hosted Cloud, services many IT providers resell to their clients. On November 18, N-able confirmed the outage was caused by a security incident: an unauthorized party got into one of the servers behind both services.
- What's down: the management portal, the API, quarantine, logging and mailbox sync, in the Americas, Europe and Asia-Pacific. Until they come back, N-able says customers may not be able to sign in, view or release quarantined messages, review logs, or add or remove domains.
- What still works: inbound and outbound email and spam filtering kept running the whole time.
- What may have been exposed: N-able told SecurityWeek the incident was isolated to a single web server, where an unauthorized party "may have been able to access certain credentials stored on the platform." It says it has no evidence that customer data or tenant mailboxes were accessed.
- What N-able did: took the server offline, rotated internal credentials, revoked customer API tokens, invalidated OAuth tokens and reset passwords for local users. As of its November 20 update, portal and API access are still disabled as a precaution.
- Separate problem, same vendor: N-able says this is unrelated to its N-central incident, where it took hosted N-central remote-management environments offline to patch a batch of zero-day flaws, which attackers are now exploiting on vulnerable servers.
Why it matters for your money
Your spam filter sits between your business and every email that arrives, so it's a vendor you trust without thinking about it. When it breaks, legitimate mail like vendor invoices, bank notices and customer requests can quietly get held in a quarantine you can't open, and nobody notices until a payment is late or a customer complains. And when a vendor says stored credentials may have been exposed, any password or connection your IT provider set up on that platform should be treated as burned until it's changed.
What to do this week
- Ask your IT provider one question: "Do we use N-able Mail Assure, SpamExperts or N-central?" If they hesitate, that's an answer too.
- Chase missing mail now. If a customer, vendor or bank says they sent something you never got, call them and have it re-sent or forwarded to another address. Don't wait for the quarantine to come back.
- Make sure credentials were changed. Since N-able revoked API tokens and reset local passwords, your provider should set new, unique ones, and change any password that was reused anywhere else.
- Watch for follow-up phishing. Scammers love fake "your quarantine has messages waiting" or "reset your email filter password" emails during a real outage. Don't click; check through your provider directly.
- Write down your email backup plan. Know who to call, how to reach your key vendors by phone, and how payment changes get verified when email can't be trusted.
Nice2GeekYou is based in San Antonio and serves all of Texas on site, and our managed IT plans cover remote clients across the U.S. We track the vendors behind your email and remote-management tools, rotate credentials when a vendor gets breached, and tell you plainly what was affected. Request a quote, see our monthly plans, or text us at (210) 504-8969.
Sources: BleepingComputer — N-able says recent security breach led to major service outage (November 20, 2026); SecurityWeek — N-able Blames Service Disruption on Cyberattack (November 20, 2026); The Hacker News — Hackers Breach N-able Cloud Server, Disrupting Email Security Management Across 3 Regions (November 19, 2026); N-able Uptime status page.